For most of the past decade, the authentication question banks asked was: Which method should we standardize on? Mobile apps provided a compelling answer, and most institutions converged on them. That question is now changing.
The challenge ahead is no longer selecting one authentication method. It is building the capability to support several at the same time.
Why a Single Method Is No Longer Sufficient
Mobile-first authentication became the dominant approach for good reasons. Following PSD2's strong customer authentication requirements, mobile apps offered banks a practical way to deliver strong authentication through biometric sensors, secure key storage, modern cryptography, and a familiar user experience. For most customers, they remain the right choice today.
The challenge is not mobile authentication itself. It is relying primarily on a single authentication approach in an environment where customer needs, accessibility requirements, and regulatory expectations continue to diversify.
PSD3/PSR makes this explicit. Banks will no longer be permitted to make strong customer authentication dependent on the exclusive use of a smartphone. The regulation requires that all customers, including those with accessibility needs, limited digital confidence, or no smartphone access, have at least one authentication method suited to their situation.
That represents an important shift. The question is no longer simply whether strong authentication is in place, but whether it works effectively for every customer who needs to use it.
The Methods Banks Will Need to Support
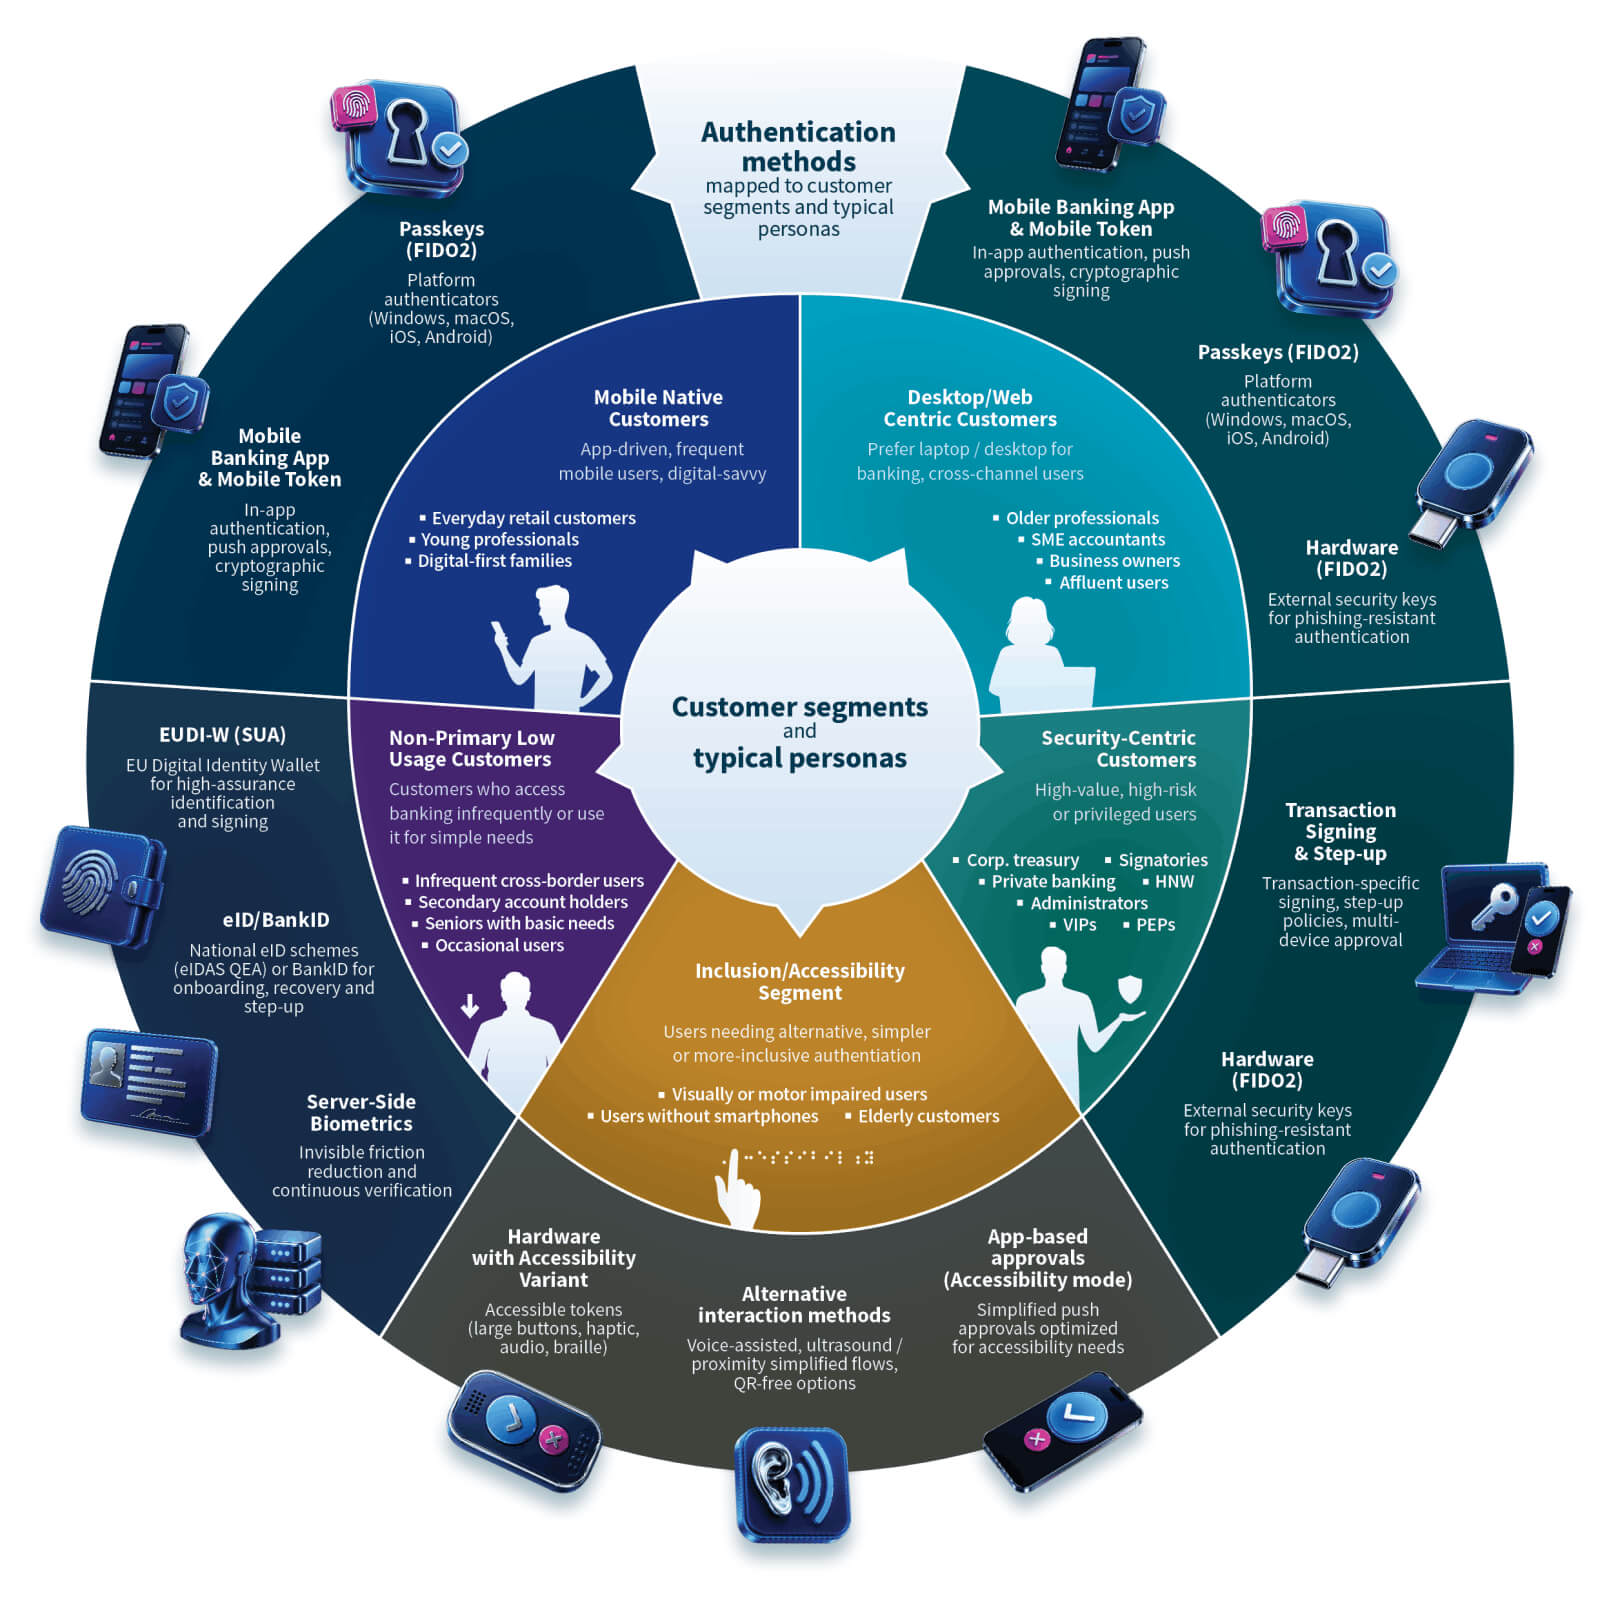
Mobile-first authentication will remain the primary option for most retail customers. However, banks will increasingly need to support a broader portfolio of authentication methods, including passkeys, FIDO2 hardware authenticators, biometric authentication, and federated identity systems such as digital identity wallets and national eID schemes.
Which method is appropriate will depend on the customer, the device they use, and the level of assurance required. Rather than replacing mobile authentication, banks will need the flexibility to support multiple authentication methods alongside it.
Flexibility as a Strategic Requirement
Supporting multiple authentication methods is not simply a product decision. It is an architectural one.
Historically, authentication was often embedded directly into individual banking applications or tightly coupled with legacy identity infrastructure. As a result, introducing a new authentication method frequently requires new integrations, duplicated business logic, extensive testing, and significant engineering effort.
Banks that have invested in flexible authentication platforms capable of supporting multiple authentication methods are in a substantially different position. For them, introducing support for a FIDO2 hardware token or integrating a digital identity wallet becomes an incremental change rather than a major transformation project.
That architectural flexibility is becoming a strategic advantage. As authentication methods continue to evolve, organizations with flexible platforms can adopt new capabilities more quickly, respond to regulatory change with less disruption, and reduce the long-term cost of modernization.
What This Means Now
Most banks are not starting from a position of full flexibility. Authentication methods are often tightly coupled to proprietary systems that were never designed to support multiple approaches.
Before introducing additional authentication methods, banks should first assess whether their current authentication platform can naturally support them or whether modernization will be required. Understanding these technology constraints early allows institutions to prioritize investments, reduce implementation risk, and avoid costly architectural dead ends.
Organizations that begin this assessment now, before regulatory deadlines become pressing and customer expectations evolve further, will have more options and more time to implement change effectively.
To learn more, download our whitepaper, which explores customer segmentation, modern authentication methods, technology considerations, and a practical roadmap for transitioning beyond a mobile-first authentication model.